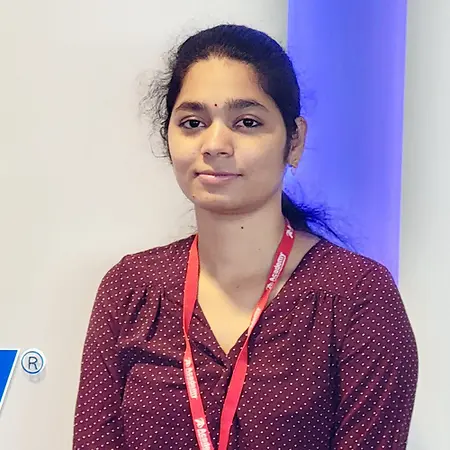
Her Story
About Rashmi
Rashmi Tallapragada is a cybersecurity and compliance professional who currently serves as a Information Protection and Security Analyst at DTE Energy. In this role, she advises leadership on security initiatives, facilitates compliance across Process Control Network and Operational Technology environments, and integrates IT standards into those settings. She also acts as her site's representative for internal and external cyber initiatives, including the annual Coast Guard inspection, and supports incident response, risk assessments, and business continuity and disaster recovery documentation. Rashmi holds a master's degree in Information System Security from the University of Houston and a bachelor's degree in Computer Science from GITAM Deemed University. Her career began at Chevron in 2019 as an IT Risk Analyst focused on the RSA Archer governance, risk, and compliance platform, and continued at Academy Sports + Outdoors, where she led risk assessments and guided PCI DSS and SOX audit efforts. Her credentials include CRISC, CISA, and Certified Information Security Professional, and her work has been recognized with a Bronze Globee Award for Cybersecurity in 2026 and selection as an Influential Woman representing Detroit, Michigan. Beyond her day-to-day responsibilities, Rashmi is active in the wider security community through ISACA and its Emerging Trends Working Group, IEEE, ACM chapters, and Women in Cybersecurity. She approaches her work with empathy and collaboration, presenting security as a partner to business teams while grounding her assessments in deep technical knowledge. Outside of work, she enjoys cooking biryani and dosa, reading, and spending time with her children.
Her Interview
Ten minutes with Rashmi
01What do you attribute your success to?
I attribute my success to the journey I have taken over the past eight years in cybersecurity and compliance. It started with my background in computer science and continued with a master’s degree focused on cybersecurity, information security, and risk. That foundation helped me understand both the technical and governance sides of security and shaped the direction of my career.
02What’s the best career advice you’ve ever received?
Early in my career, my manager, Mike Callely, taught me the importance of approaching business teams with a polite and helpful mindset and showing them that security can be an ally rather than a burden. Later, Victor Springer, a refinery manager, encouraged me to look at security from an incident perspective and go beyond checklists by understanding the underlying systems, assets, and inventory. Those lessons shaped how I approach risk today, combining technical understanding with practical decisions that protect the organization while supporting the business.
03What advice would you give to young women entering your industry?
Build strong professional connections and decide early which area of cybersecurity you want to pursue, because the field is very broad. For those interested in governance, risk, and compliance, develop a strong understanding of major frameworks, pursue relevant ISACA certifications, and look for opportunities to gain hands-on experience. Writing policies, performing risk assessments, supporting audits, and working directly with business teams can help turn theoretical knowledge into practical expertise.
04What are the biggest challenges or opportunities in your field right now?
One of the biggest challenges in cybersecurity and compliance is interpreting requirements, because frameworks such as NIST can be understood and applied differently depending on the organization. Standardizing policies and expectations is important, but it is equally important to understand your own environment, including its systems, tools, capabilities, and limitations. Good security decisions should be grounded not only in frameworks and checklists, but also in the technical realities of the environment and the risks the organization actually faces.
05What values are most important to you in your work and personal life?
In my work, I value ensuring compliance, performing thorough access, configuration, and change management reviews, keeping data aligned with audit requirements, and working collaboratively with teams to address deficiencies. I also believe empathy matters, especially when working with busy business partners. Clear communication and documentation can make security requirements much easier for non-technical stakeholders to understand and act upon.
Outside of work, most of my time revolves around my children and family. I love cooking for them, especially dishes like biryani and dosa, and I enjoy the simple moments we spend together. I also enjoy reading and learning new things, whether they relate to my profession or simply spark my curiosity. Those quieter parts of my life help me recharge and bring balance to the fast-moving world of cybersecurity.
Join Influential Women and start making an impact. Register now.