THE IDENTITY GOVERNANCE TRIBUNE
How AI agents are forcing identity governance and privileged access management to finally converge.
Two significant moves landed in the identity market this week within days of each other. Omada Identity acquired EmpowerID to bring real-time, runtime authorization directly into its IGA platform. Keeper Security and SailPoint announced a deep integration linking SailPoint's IGA engine to KeeperPAM's privileged credential management, automating provisioning, access certifications, and revocations across privileged accounts.
Taken individually, each is a meaningful product story. Taken together, they are a market-wide signal: the long-standing separation between identity governance and privileged access management is ending, and the organizations still treating them as separate programs are accumulating a governance debt that AI agent proliferation is about to make very expensive.
THE DEAL THAT EXPLAINS THE DECADE
The IGA and PAM markets developed in parallel for good reason. IGA solved the "who should have access and why" question: access request workflows, role management, certification campaigns, and policy enforcement. PAM solved the "how do we protect the most dangerous credentials" question: privileged session management, password vaulting, just-in-time access, and least-privilege enforcement. They were different problems, different buyers, different vendors, and different budgets.
The problem is that AI agents do not respect that organizational chart. An AI agent that is provisioned through an IGA workflow, authenticates via a service account managed by a PAM tool, and executes actions in a production environment through an API key that lives in neither system does not fit neatly into either program. It lives in the gap between them, and that gap is now the largest ungoverned surface in the enterprise.
The Omada/EmpowerID acquisition and the Keeper/SailPoint integration both address that gap from different angles. Omada is bringing runtime authorization—the ability to enforce access decisions at the moment of execution, not just at the moment of provisioning—inside its IGA platform. SailPoint and Keeper are closing the loop between access approval and credential control, so that when IGA says, "This access should be revoked," PAM actually enforces it automatically, not on the next manual audit cycle.
"Governance without enforcement is just paperwork. What this week's deals confirmed is that the market has finally run out of patience with systems that say what should happen but cannot guarantee that it does."
WHAT THE NUMBERS ARE SAYING
According to Keeper Security's own research published alongside the integration announcement, 96% of senior IT leaders say disconnected security tools are creating exploitable gaps. That number is not surprising—but the context matters. These are not gaps in detection or gaps in policy. They are gaps in execution: situations where a governance decision exists but cannot be enforced because the system that made the decision and the system that controls the credential do not talk to each other.
Saviynt's data adds the AI-specific dimension: 92% of organizations report limited visibility into AI agent identities, and 53% say AI agents already exceed their intended permissions. The combination is precise: organizations are provisioning AI agents they cannot see, through workflows not designed for them, into environments where no enforcement mechanism exists to catch drift.
■ BY THE NUMBERS
96% — Senior IT leaders who say disconnected security tools create exploitable gaps (Keeper Security, 2026)
92% — Organizations reporting limited visibility into AI agent identities (Saviynt, 2026)
53% — Organizations where AI agents already exceed their intended permissions (Saviynt, 2026)
80:1 — Non-human to human identity ratio in the average enterprise (CyberArk, 2024)
#1 — Compliance readiness: top driver for IGA modernization investment in 2026 (GigaOm / KuppingerCole, 2026)
KUPPINGERCOLE NAMES THE DIVIDING LINE
In its 2026 Identity & Access Governance Leadership Compass, presented by Nitish Deshpande in a September 16 webinar, KuppingerCole identified a clear dividing line between IGA leaders and laggards in the current market cycle: whether NHI governance and identity correlation are treated as core platform capabilities or as optional add-ons. Vendors that have made NHI governance structural—not bolted on—are consistently outperforming those that have not, both in customer outcomes and in market positioning.
Deshpande also previewed an October 1 follow-up webinar with a title that practitioners are already sharing on LinkedIn: "The Audit Binder Is Not a Security Strategy." The title does the argument for him. Point-in-time audit evidence assembled manually before an examination is not the same thing as a governed environment. The organizations that will hold up under regulatory pressure are the ones generating audit evidence automatically, continuously, as a byproduct of how they operate—not as a project they run before someone shows up to look.
"The audit binder is not a security strategy."
— KuppingerCole (Nitish Deshpande), webinar title preview, October 1, 2026
SAILPOINT FRAMES THE AGENTIC MANDATE
SailPoint this week published its strategic distillation of IdentityTV 2026: five mandates it argues define what identity governance must look like in the agentic economy:
- Treat every AI agent as a first-class identity — with an owner, a lifecycle, and a defined entitlement set.
- Move from static to adaptive governance — reviews triggered by behavior and context, not by calendar.
- Stop agents from inheriting human credentials — dedicated, scoped, expiring credentials only.
- Apply risk-tiered application onboarding — not every app needs the same governance depth, but every app needs some.
- Enforce Zero Standing Privilege at scale — no persistent elevated access, human or non-human.
These are not aspirational principles. Each one corresponds to a capability gap that the SailPoint/Keeper integration and the Omada/EmpowerID acquisition are directly designed to close.
WHAT PRACTITIONERS SHOULD BE ASKING RIGHT NOW
The week's news raises one practical question for every IGA practitioner: when your IGA platform makes a governance decision—revoke this access, narrow this entitlement, flag this anomaly—what actually happens next? Is that decision enforced automatically? Does it reach the PAM system that controls the credential? Does it cover service accounts and API keys, or only human accounts? And is there an auditable record of the enforcement, not just the decision?
If any of those answers is "we handle that manually" or "that's a separate system," the gap is named. The question is whether you close it on your own terms or wait for an incident or an audit finding to close it for you.
THIS WEEK IN IDENTITY: PODCASTS WORTH YOUR TIME
🎙 Identity at the Center — Ep. #449: "Transaction Tokens with George Fletcher" (Sept. 21)
George Fletcher joins Jeff Steadman and Sean O'Dell for a deep technical dive into OAuth Transaction Tokens (Txn-Tokens), the IETF spec designed to secure requests as they flow across microservices and AI agent chains. Core relevance for IGA practitioners: session termination and privilege scoping must extend beyond disabling an account—they must follow the request chain.
🎙 Identity at the Center — Ep. #450: "New to Identity with Alexis Bernthal" (Sept. 28 — out this morning)
RSM technology risk consultant Alexis Bernthal talks about breaking into IAM, role-based access as an on-ramp topic, and what agentic identity sessions at Identiverse 2026 looked like from a first-time attendee's perspective.
🎙 The Analyst Brief — Ep. #75: "Identiverse 2026: Agentic AI, NHI Security & the Future of Identity Platforms" (Simon Moffatt & David Mahdi)
Still the essential listen this week. Simon and David unpack agentic identity governance, NHI security, and what SailPoint/Entro and Cisco/WideField signal about the convergence of IGA, PAM, and ITDR into a single identity security platform category.
📅 MARK YOUR CALENDAR
Oct. 1, 2026 — KuppingerCole Webinar: "The Audit Binder Is Not a Security Strategy" (Nitish Deshpande) → kuppingercole.com
Oct. 1–3, 2026 — Gartner Identity & Access Management Summit, Las Vegas → gartner.com/en/conferences
Sept. 15–Nov. 20, 2026 — Saviynt UNLOCK 2026 Global Roadshow (12 cities) → saviynt.com/unlock
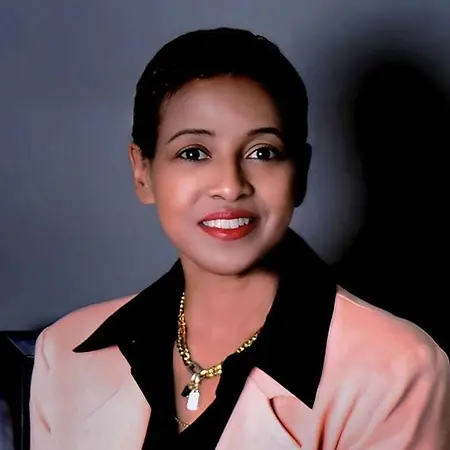
Carol Griffin is a technology, security, and telecommunications leader with more than two decades of experience guiding large‑scale infrastructure, identity, and cloud modernization programs. She is the Founder of ROSE Tech Academy LLC, a Microsoft Security Advisor in the Microsoft Community’s private NDA program, and a Technical Thought Speaker with the Microsoft Speakers Hub. Carol spent 25 years at AT&T,…